Attribute Injection leading to XSS(Cross-Site-Scripting) in uptime-kuma
cve-program · CVE-2023-49276
PublishedUptime Kuma is an open source self-hosted monitoring tool. In affected versions the Google Analytics element in vulnerable to Attribute Injection leading to Cross-Site-Scripting (XSS). Since the custom status interface can set an independent Google Analytics ID and the template has not been sanitized, there is an attribute injection vulnerability here, which can lead to XSS attacks. This vulnerability has been addressed in commit `f28dccf4e` which is included in release version 1.23.7. Users are advised to upgrade. There are no known workarounds for this vulnerability.
Read the publisher's advisoryeuvd · EUVD-2023-3036
PublishedUptime Kuma is an open source self-hosted monitoring tool. In affected versions the Google Analytics element in vulnerable to Attribute Injection leading to Cross-Site-Scripting (XSS). Since the custom status interface can set an independent Google Analytics ID and the template has not been sanitized, there is an attribute injection vulnerability here, which can lead to XSS attacks. This vulnerability has been addressed in commit `f28dccf4e` which is included in release version 1.23.7. Users are advised to upgrade. There are no known workarounds for this vulnerability.
Read the publisher's advisorynvd · CVE-2023-49276
PublishedUptime Kuma is an open source self-hosted monitoring tool. In affected versions the Google Analytics element in vulnerable to Attribute Injection leading to Cross-Site-Scripting (XSS). Since the custom status interface can set an independent Google Analytics ID and the template has not been sanitized, there is an attribute injection vulnerability here, which can lead to XSS attacks. This vulnerability has been addressed in commit `f28dccf4e` which is included in release version 1.23.7. Users are advised to upgrade. There are no known workarounds for this vulnerability.
Read the publisher's advisoryosv · GHSA-v4v2-8h88-65qj
Published### Summary Google Analytics element Attribute Injection leading to XSS ### Details Since the custom status interface can set an independent Google Analytics ID and the template has not been sanitized, there is an attribute injection vulnerability here, which can lead to XSS attacks. 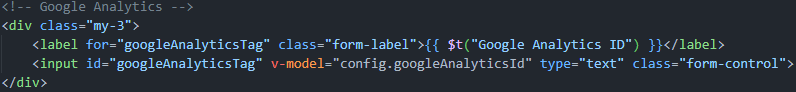 ### PoC 1. Run the latest version of the louislam/uptime-kuma container and initialize the account password. 2. Create a new status page. 3. Edit the status page and change the Google Analytics ID to following payload(it only works for firefox. Any attribute can be injected, but this seems the most intuitive): ``` 123123" onafterscriptexecute=alert(window.name+1),eval(window.name) a="x ``` 4. Click Save and return to the interface. XSS occurs. screenshots:  
Read the publisher's advisoryAffected versions, risk and source history
Related advisories and sources
Publishers link these advisories through the identifiers shown below. A shared identifier or date alone does not tell you whether your software is affected or whether the advisories describe the same cause.
CVE-2023-49276 · CVE overview and exploitation status
cve-program · CVE-2023-49276
- https://github.com/louislam/uptime-kuma/security/advisories/GHSA-v4v2-8h88-65qj
- https://github.com/louislam/uptime-kuma/commit/f28dccf4e11f041564293e4f407e69ab9ee2277f
euvd · EUVD-2023-3036
- https://github.com/louislam/uptime-kuma/security/advisories/GHSA-v4v2-8h88-65qj
- https://github.com/louislam/uptime-kuma/commit/f28dccf4e11f041564293e4f407e69ab9ee2277f
nvd · CVE-2023-49276
- https://github.com/louislam/uptime-kuma/commit/f28dccf4e11f041564293e4f407e69ab9ee2277f
- https://github.com/louislam/uptime-kuma/security/advisories/GHSA-v4v2-8h88-65qj
osv · GHSA-v4v2-8h88-65qj
Related changes
Linked by CVE identifierNo related changes are available here.