1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.
1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.
1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.
### Impact
The steps are as follows:
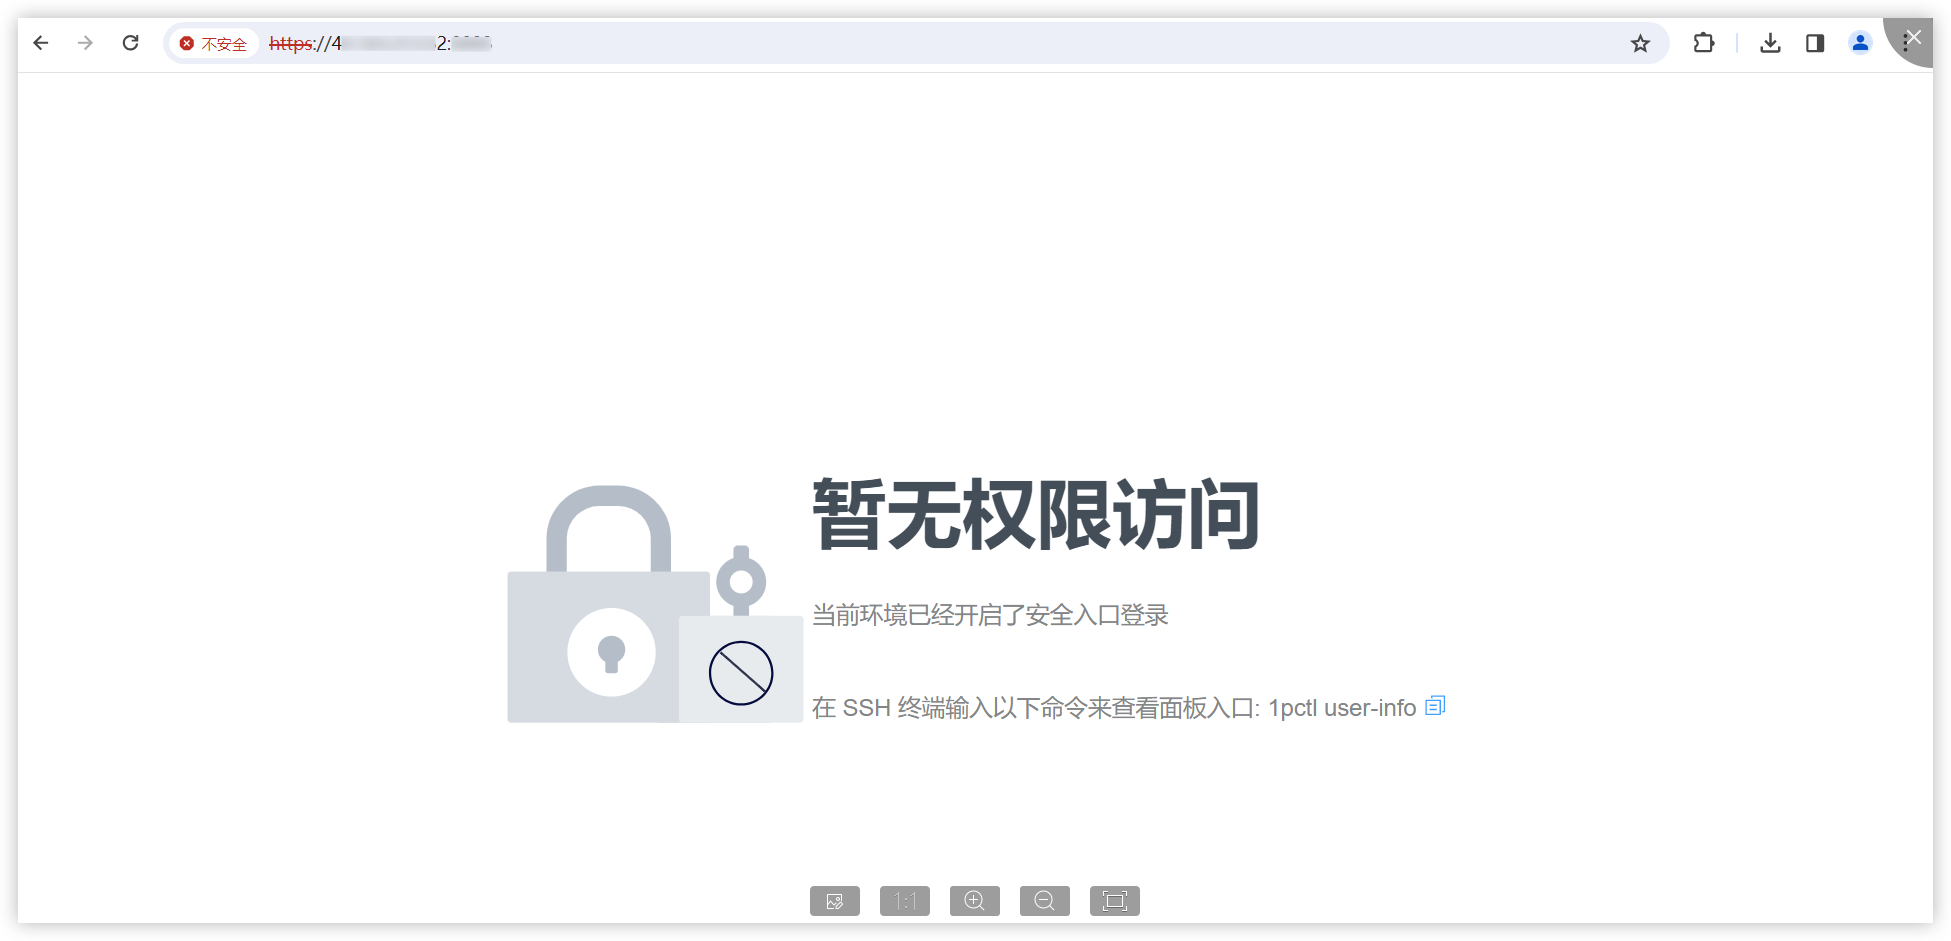
1. Access https://IP:PORT/ in the browser, which prompts the user to access with a secure entry point.
2. Use Burp to intercept:
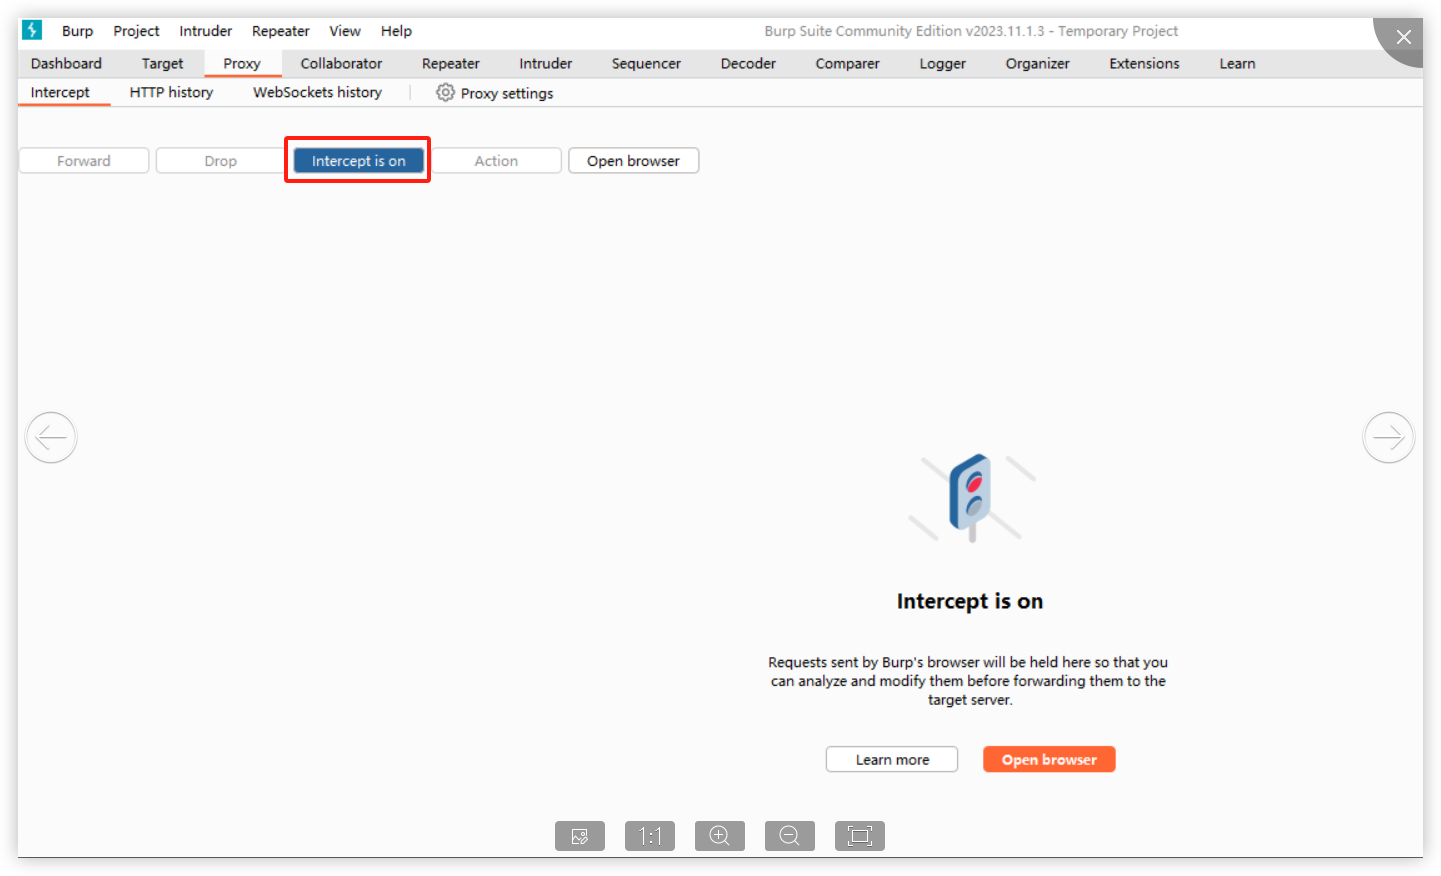
When opening the browser and entering the URL (allowing the first intercepted packet through Burp), the following is displayed:
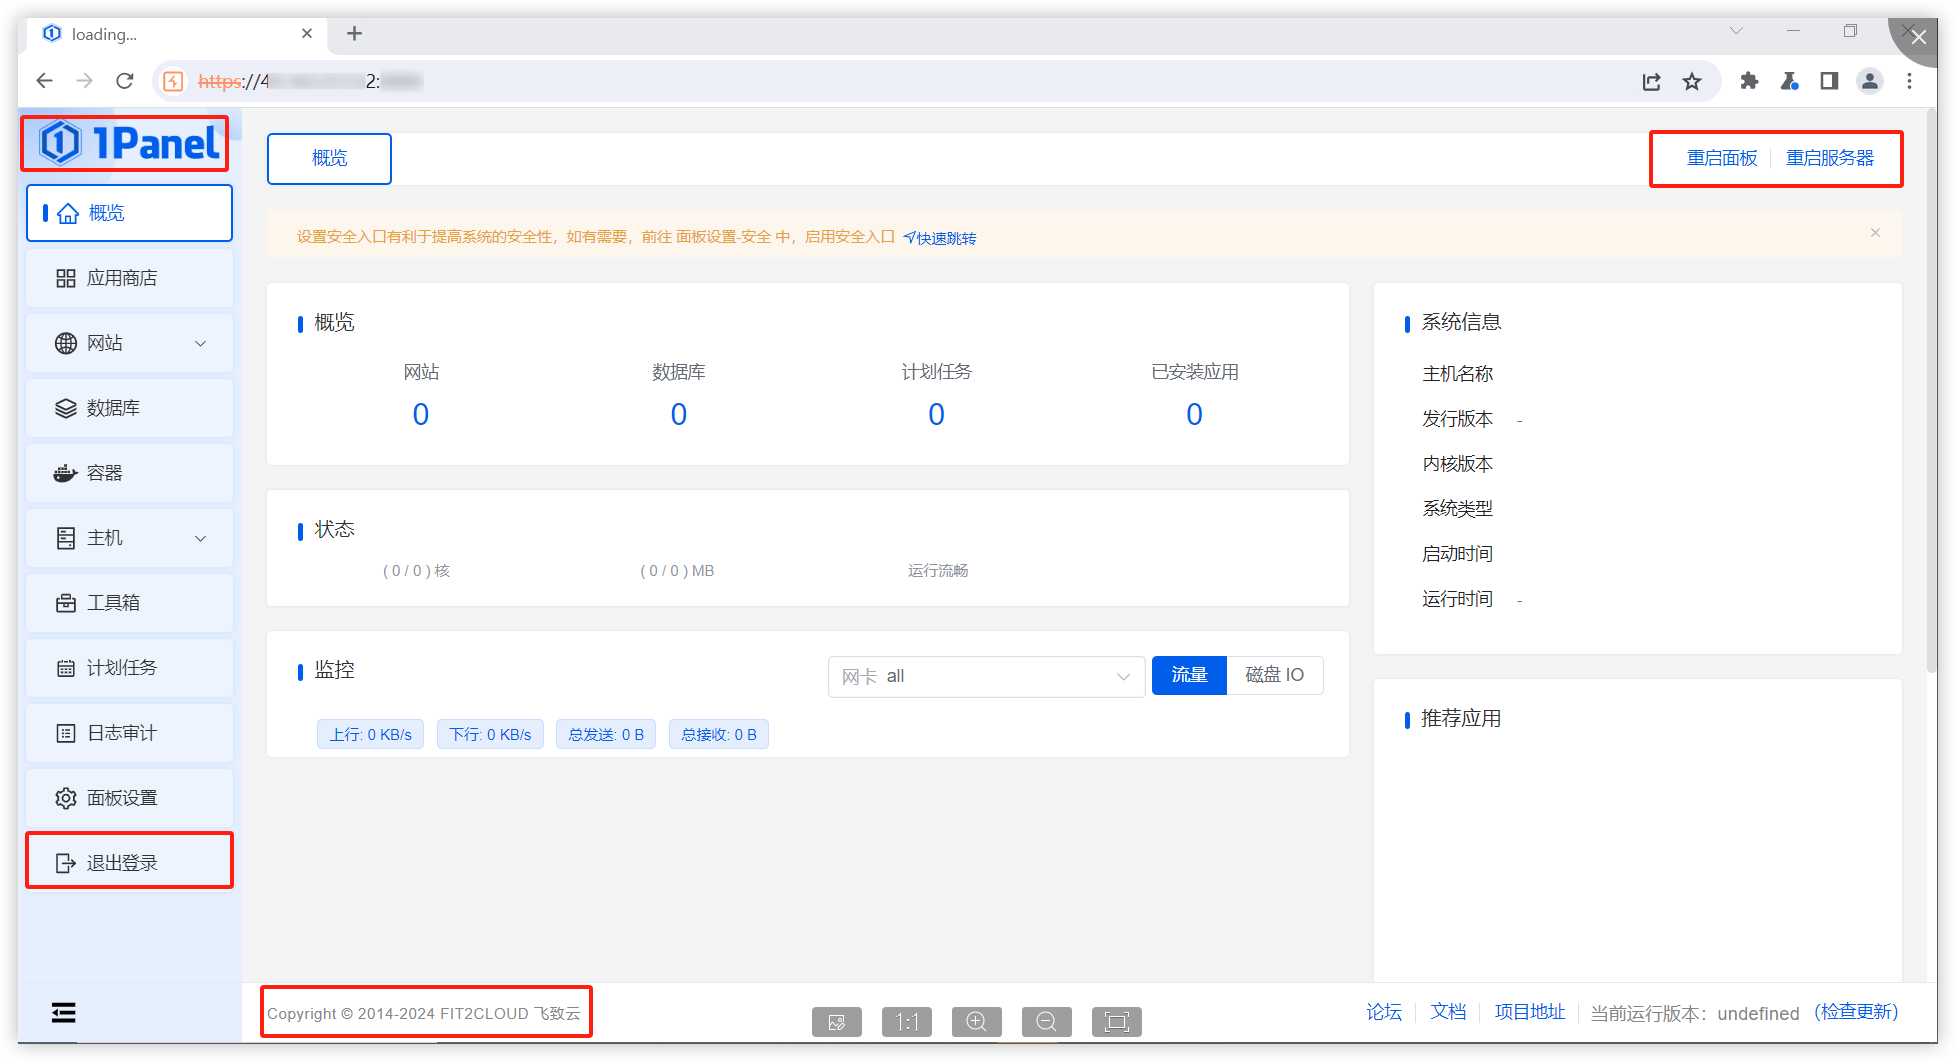
It is found that in this situation, we can access the console page (although no data is returned and no modification operations can be performed)."
Affected versions: <= 1.10.0-lts
### Patches
The vulnerability has been fixed in v1.10.1-lts.
### Workarounds
It is recommended to upgrade the version to 1.10.1-lts.
### References
If you have any questions or comments about this advisory:
Open an issue in https://github.com/1Panel-dev/1Panel
Email us at [email protected]
If the user attempts to access a secure entry point and intercepts with Burp, they can get access to the console page. This access does not return data nor allow modification operations.
EUVD source date text has no stated timezone and is retained without inventing a UTC instant. Related bulletin membership is not an alias, common cause or applicability claim. A missing vector with a zero score is treated as unrated. Complete vendor/product and underlying source evidence remains in the original JSON.
Original publisher date fields
datePublished: Mar 6, 2024, 6:23:50 PM
dateUpdated: Aug 27, 2024, 4:52:53 PM
No normalized affected-package data is projected for this source revision. The original publisher record may contain additional product and version evidence; this does not establish that a package is unaffected.
NVD analysis and CPE criteria are source context, not proof that a package or your environment is affected. Complete affected data, logical configurations and SSVC are retained in the original JSON.
Source analysis status: Analyzed
Weakness classifications: CWE-863
Original publisher date fields
published: 2024-03-06T19:15:07.933
lastModified: 2026-06-17T07:19:34.880
1 source CPE criteria · context only
cpe:2.3:a:fit2cloud:1panel:*:*:*:*:*:*:*:*
The original JSON retains the logical configuration operators, exclusions and version bounds.
No normalized affected-package data is projected for this source revision. The original publisher record may contain additional product and version evidence; this does not establish that a package is unaffected.