1Panel open source panel project has an unauthorized vulnerability.
cve-program · CVE-2024-27288
Published1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.
Read the publisher's advisoryeuvd · EUVD-2024-0784
Published1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.
Read the publisher's advisorynvd · CVE-2024-27288
Published1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.
Read the publisher's advisoryosv · GHSA-26w3-q4j8-4xjp
Published### Impact The steps are as follows: 1. Access https://IP:PORT/ in the browser, which prompts the user to access with a secure entry point. 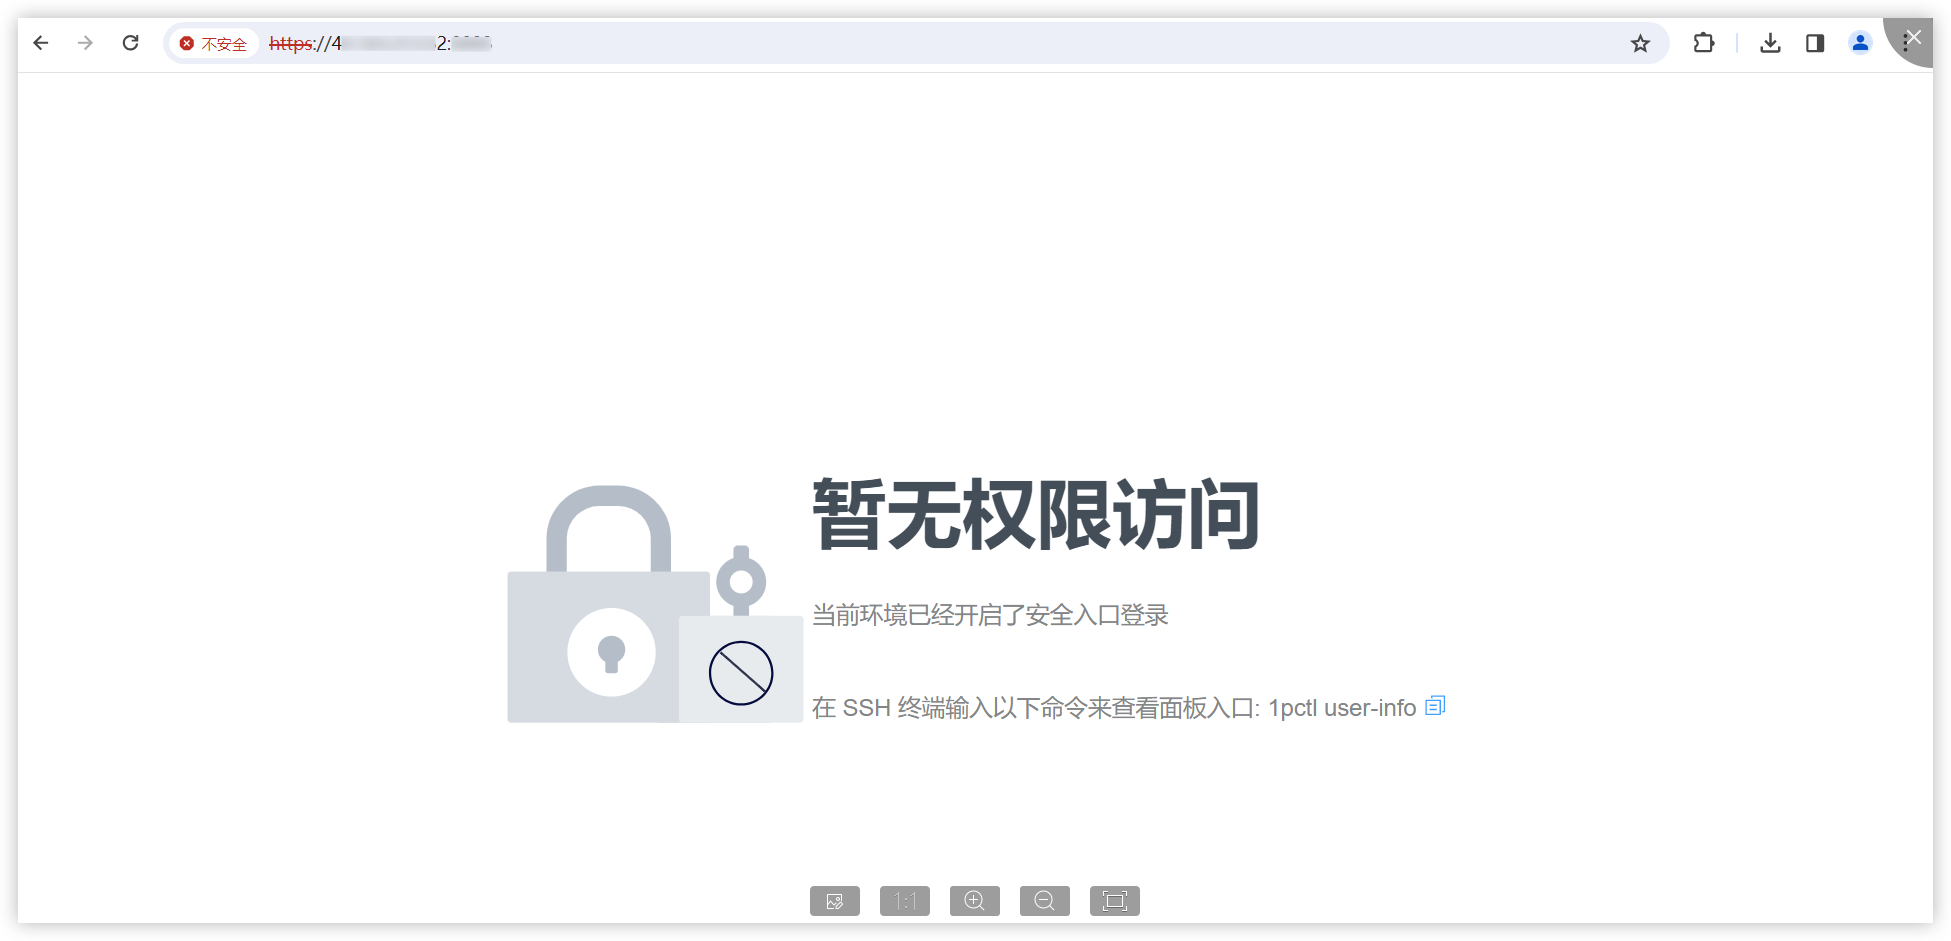 2. Use Burp to intercept: 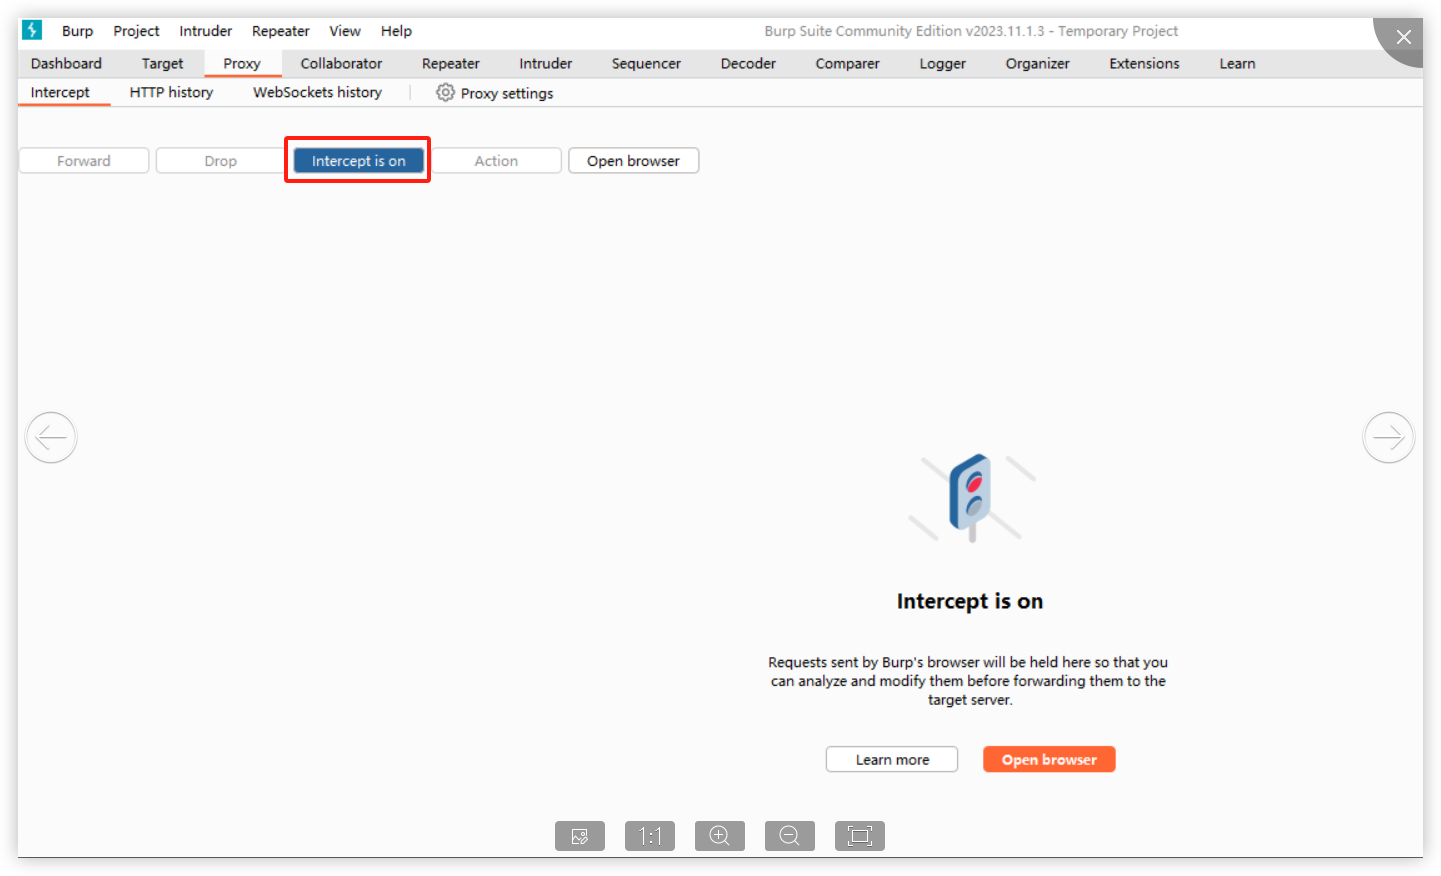 When opening the browser and entering the URL (allowing the first intercepted packet through Burp), the following is displayed: 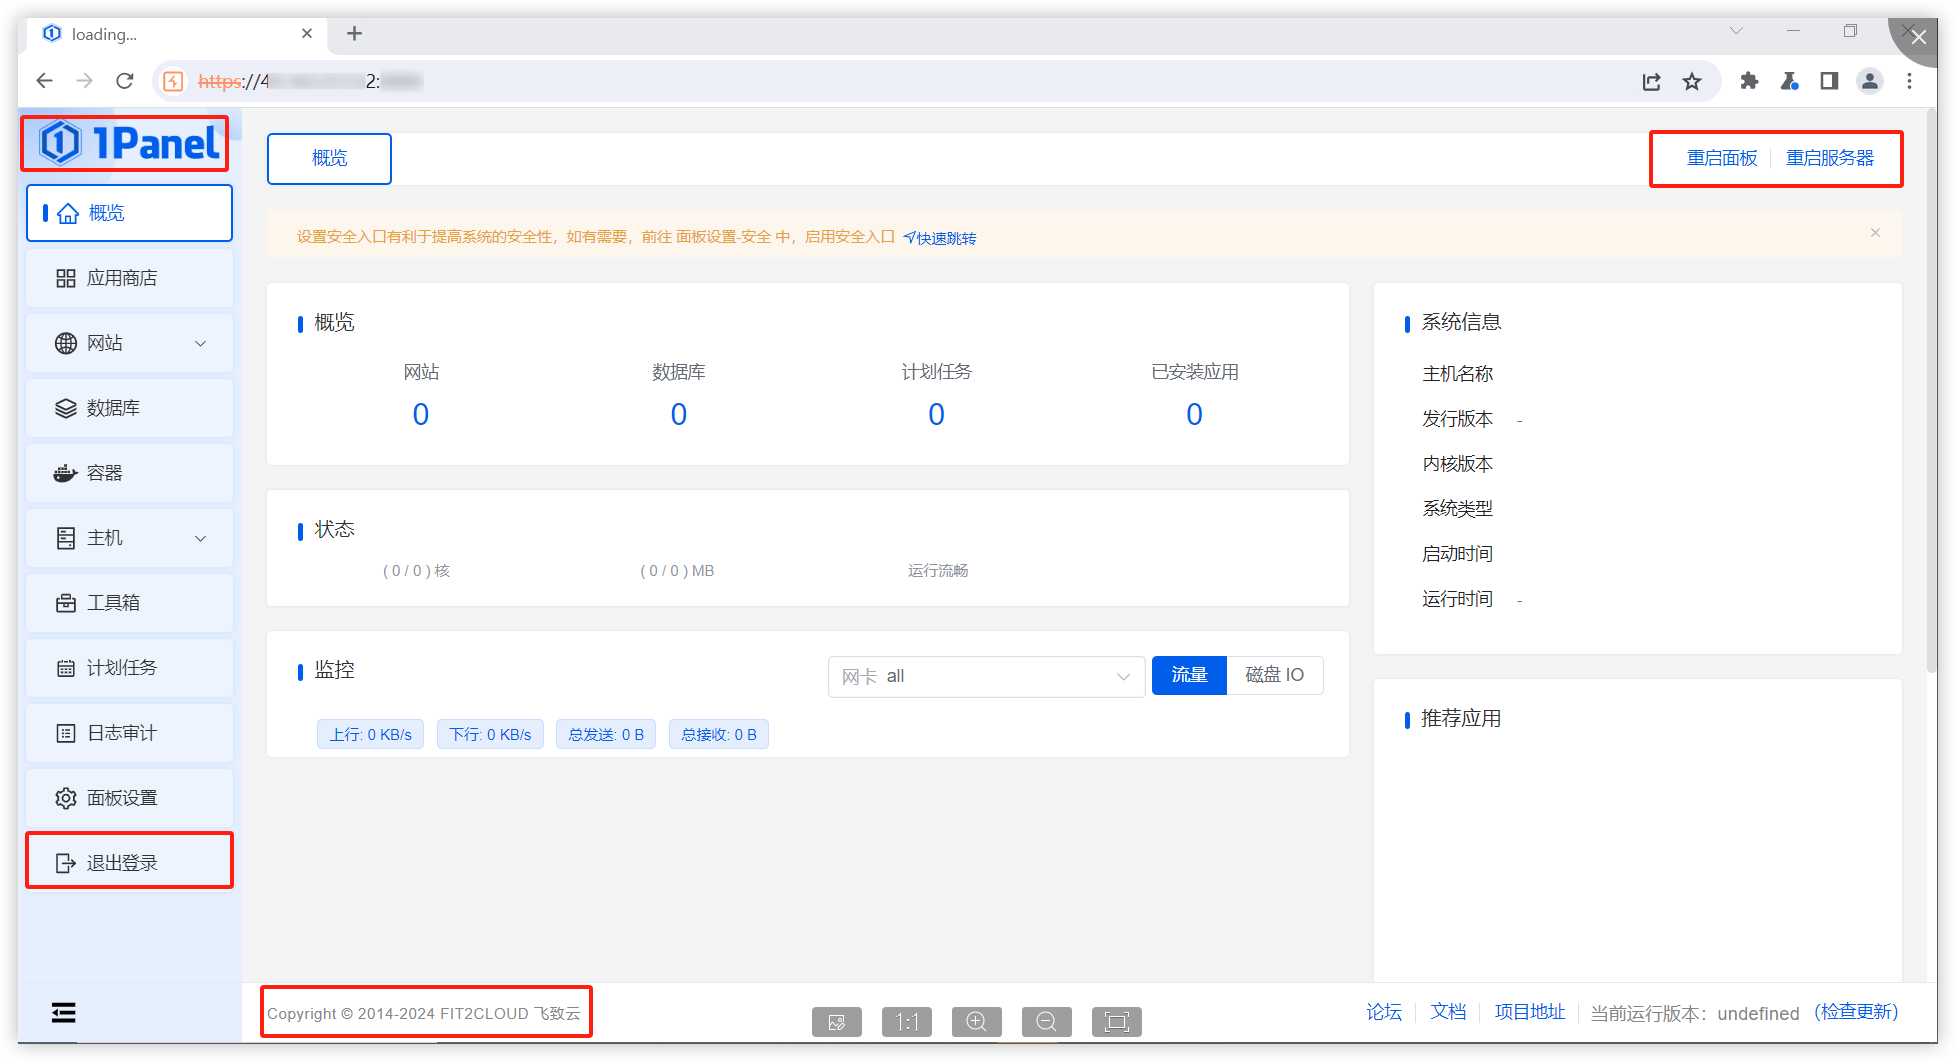 It is found that in this situation, we can access the console page (although no data is returned and no modification operations can be performed)." Affected versions: <= 1.10.0-lts ### Patches The vulnerability has been fixed in v1.10.1-lts. ### Workarounds It is recommended to upgrade the version to 1.10.1-lts. ### References If you have any questions or comments about this advisory: Open an issue in https://github.com/1Panel-dev/1Panel Email us at [email protected]
Read the publisher's advisoryosv · GO-2024-2613
PublishedIf the user attempts to access a secure entry point and intercepts with Burp, they can get access to the console page. This access does not return data nor allow modification operations.
Read the publisher's advisoryAffected versions, risk and source history
Exploitation and risk
Source statusCISA KEV lists vulnerabilities known to be exploited. FIRST EPSS estimates the likelihood of exploitation in the next 30 days. An unavailable score does not mean zero risk.
Which CVEs have scores here?
This view includes predictions for CVE identifiers explicitly listed in public NuGet advisories. Microsoft release pages have their own prediction coverage. Check source status for the scope and latest checks.
No exploitation or prediction data is available here for these CVEs. This does not mean they are safe or unlikely to be exploited.
cve-program · CVE-2024-27288
Published1Panel open source panel project has an unauthorized vulnerability.
1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.
- Source published
- 6 Mar 2024 18:23:50 UTC
- Source modified
- 27 Aug 2024 16:52:53 UTC
- Saved here
- 23 Oct 2026 15:48:27 UTC
- Source terms
- CVE Program Terms of Use
Original source record · Cite this exact observation · Complete original publisher JSON
Source: cve-program · CVE Program Terms of Use. The publisher's wording is preserved. ChangeIntel groups the information and labels changes. The JSON record includes additional source fields.
CVSS 3.1 · 6.3 CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L
euvd · EUVD-2024-0784
Published1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are …
1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.
Additional publisher context
EUVD source date text has no stated timezone and is retained without inventing a UTC instant. Related bulletin membership is not an alias, common cause or applicability claim. A missing vector with a zero score is treated as unrated. Complete vendor/product and underlying source evidence remains in the original JSON.
Original publisher date fields
datePublished: Mar 6, 2024, 6:23:50 PM
dateUpdated: Aug 27, 2024, 4:52:53 PM
- Source published
- Mar 6, 2024, 6:23:50 PM (timezone not stated)
- Source modified
- Aug 27, 2024, 4:52:53 PM (timezone not stated)
- Saved here
- 15 Nov 2026 01:52:16 UTC
- Source terms
- ENISA EUVD · source terms and attribution apply
Original source record · Cite this exact observation · Complete original publisher JSON
Source: euvd · ENISA EUVD · source terms and attribution apply. The publisher's wording is preserved. ChangeIntel groups the information and labels changes. The JSON record includes additional source fields.
EUVD CVSS 3.1 · 6.3 CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L
nvd · CVE-2024-27288
Published1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are …
1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.
Additional publisher context
NVD analysis and CPE criteria are source context, not proof that a package or your environment is affected. Complete affected data, logical configurations and SSVC are retained in the original JSON.
Source analysis status: Analyzed
Weakness classifications: CWE-863
Original publisher date fields
published: 2024-03-06T19:15:07.933
lastModified: 2026-06-17T07:19:34.880
1 source CPE criteria · context only
- cpe:2.3:a:fit2cloud:1panel:*:*:*:*:*:*:*:*
The original JSON retains the logical configuration operators, exclusions and version bounds.
- Source published
- 6 Mar 2024 19:15:07 UTC
- Source modified
- 17 Jun 2026 07:19:34 UTC
- Saved here
- 24 Oct 2026 23:17:28 UTC
- Source terms
- NIST NVD usage terms; underlying source attribution retained
Original source record · Cite this exact observation · Complete original publisher JSON
Source: nvd · NIST NVD usage terms; underlying source attribution retained. The publisher's wording is preserved. ChangeIntel groups the information and labels changes. The JSON record includes additional source fields.
CVSS 3.1 · [email protected] · Secondary · 6.3 CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L
CVSS 3.1 · [email protected] · Primary · 3.1 CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:U/C:L/I:N/A:N
osv · GHSA-26w3-q4j8-4xjp
Published1Panel open source panel project has an unauthorized vulnerability.
### Impact The steps are as follows: 1. Access https://IP:PORT/ in the browser, which prompts the user to access with a secure entry point.  2. Use Burp to intercept:  When opening the browser and entering the URL (allowing the first intercepted packet through Burp), the following is displayed:  It is found that in this situation, we can access the console page (although no data is returned and no modification operations can be performed)." Affected versions: <= 1.10.0-lts ### Patches The vulnerability has been fixed in v1.10.1-lts. ### Workarounds It is recommended to upgrade the version to 1.10.1-lts. ### References If you have any questions or comments about this advisory: Open an issue in https://github.com/1Panel-dev/1Panel Email us at [email protected]
- Source published
- 6 Mar 2024 15:29:11 UTC
- Source modified
- 10 Sep 2026 03:50:00 UTC
- Saved here
- 24 Oct 2026 13:19:41 UTC
- Source terms
- GitHub Advisory Database · CC-BY-4.0
Original source record · Cite this exact observation · Complete original publisher JSON
Source: osv · GitHub Advisory Database · CC-BY-4.0. The publisher's wording is preserved. ChangeIntel groups the information and labels changes. The JSON record includes additional source fields.
CVSS_V3 · CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:L/I:L/A:L
Publisher rating · MODERATE
osv · GO-2024-2613
PublishedUnauthorized Console access in github.com/1Panel-dev/1Panel
If the user attempts to access a secure entry point and intercepts with Burp, they can get access to the console page. This access does not return data nor allow modification operations.
- Source published
- 14 Mar 2024 17:12:53 UTC
- Source modified
- 3 Mar 2026 04:54:51 UTC
- Saved here
- 24 Oct 2026 13:19:41 UTC
- Source terms
- OSV · upstream source license applies
Original source record · Cite this exact observation · Complete original publisher JSON
Source: osv · OSV · upstream source license applies. The publisher's wording is preserved. ChangeIntel groups the information and labels changes. The JSON record includes additional source fields.