1Panel open source panel project has an unauthorized vulnerability.
cve-program · CVE-2024-27288
Published1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.
Read the publisher's advisoryeuvd · EUVD-2024-0784
Published1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.
Read the publisher's advisorynvd · CVE-2024-27288
Published1Panel is an open source Linux server operation and maintenance management panel. Prior to version 1.10.1-lts, users can use Burp to obtain unauthorized access to the console page. The vulnerability has been fixed in v1.10.1-lts. There are no known workarounds.
Read the publisher's advisoryosv · GHSA-26w3-q4j8-4xjp
Published### Impact The steps are as follows: 1. Access https://IP:PORT/ in the browser, which prompts the user to access with a secure entry point. 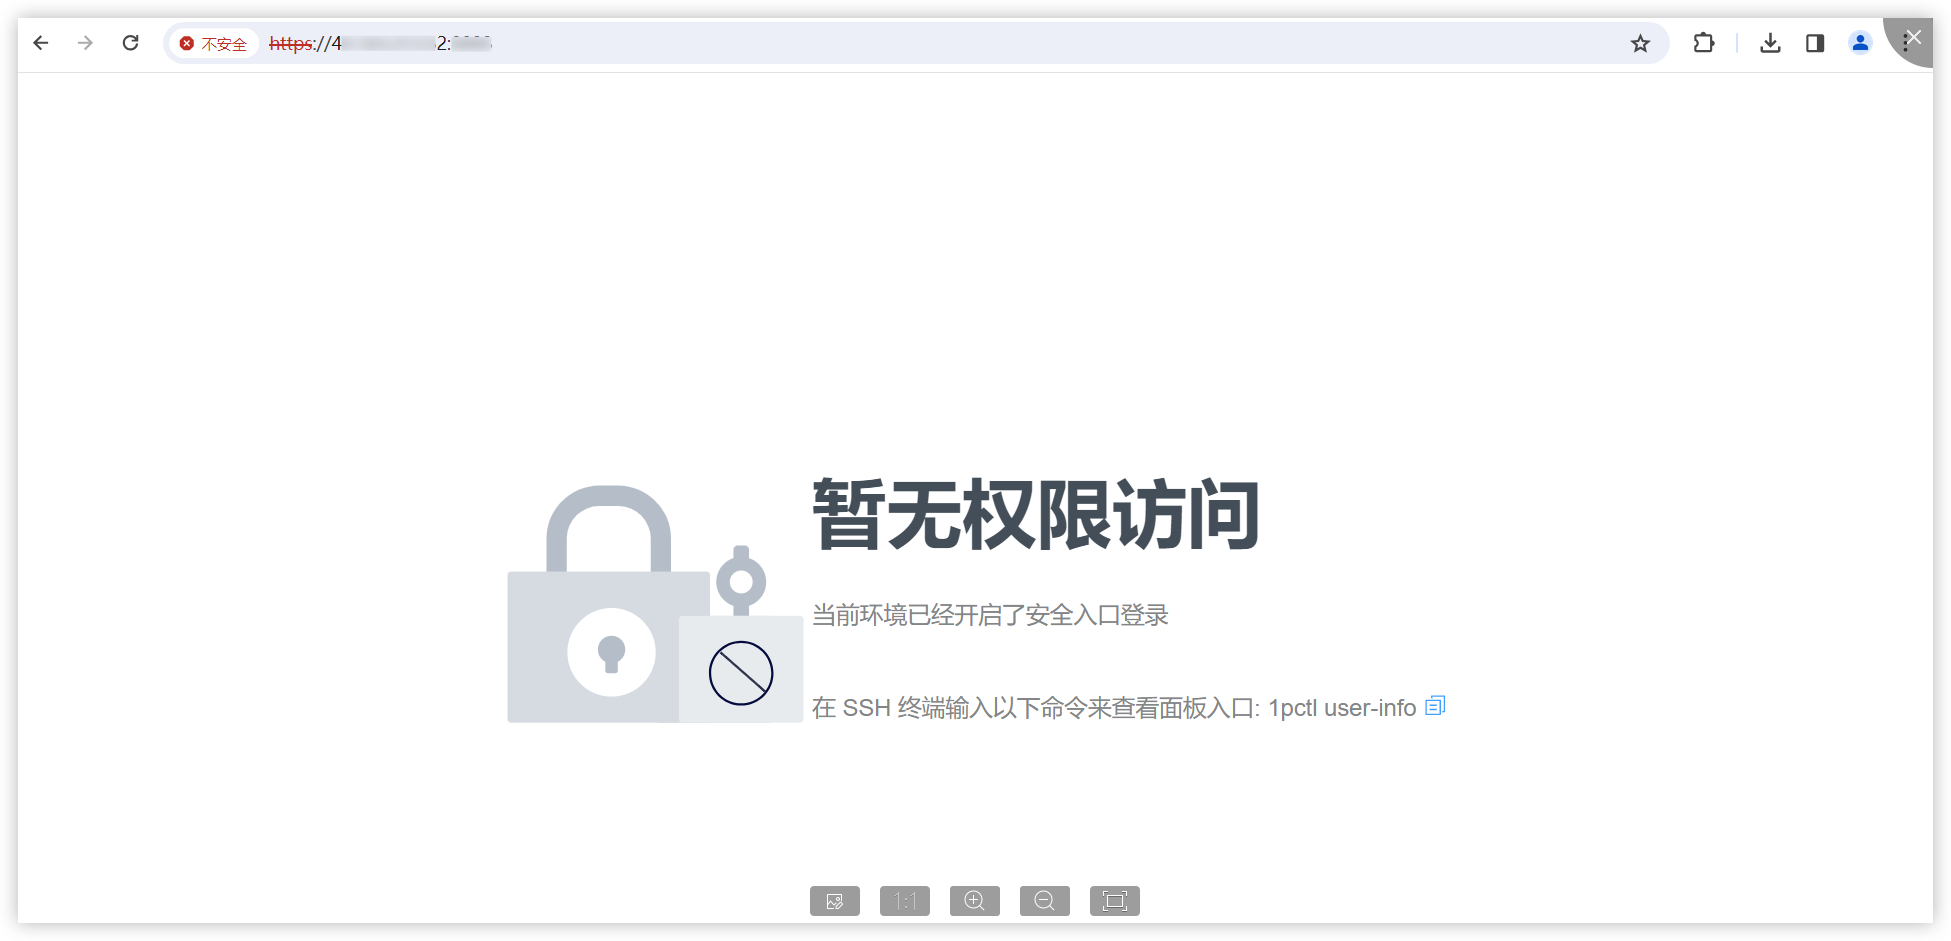 2. Use Burp to intercept: 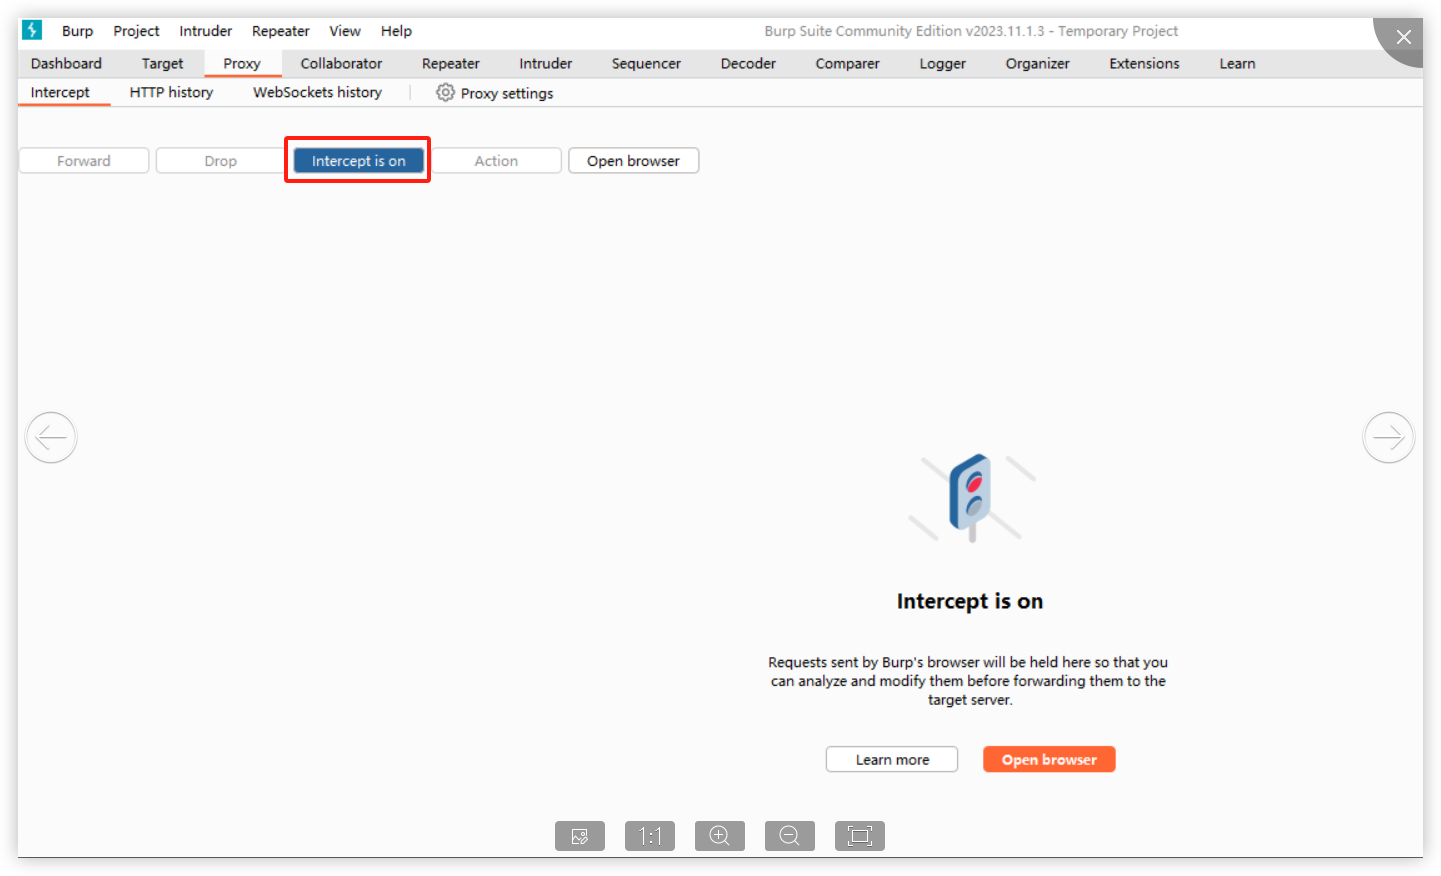 When opening the browser and entering the URL (allowing the first intercepted packet through Burp), the following is displayed: 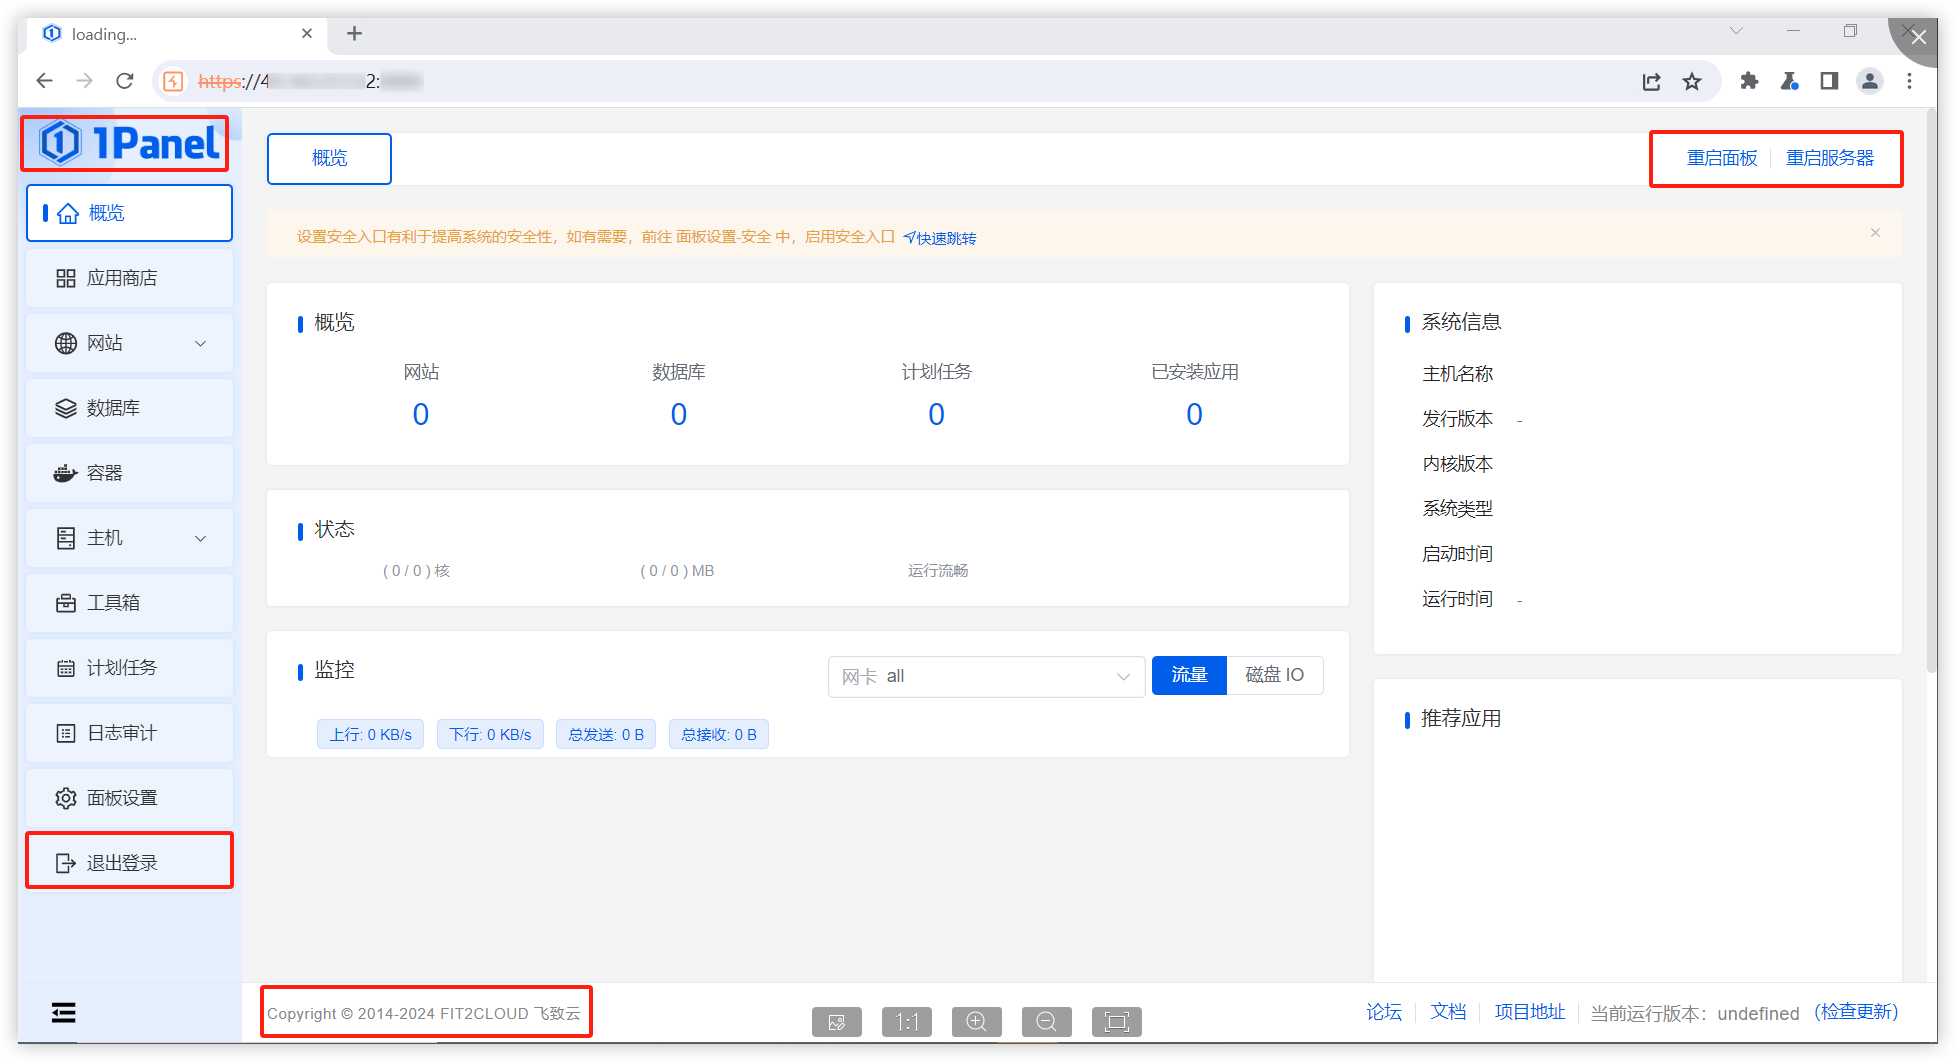 It is found that in this situation, we can access the console page (although no data is returned and no modification operations can be performed)." Affected versions: <= 1.10.0-lts ### Patches The vulnerability has been fixed in v1.10.1-lts. ### Workarounds It is recommended to upgrade the version to 1.10.1-lts. ### References If you have any questions or comments about this advisory: Open an issue in https://github.com/1Panel-dev/1Panel Email us at [email protected]
Read the publisher's advisoryosv · GO-2024-2613
PublishedIf the user attempts to access a secure entry point and intercepts with Burp, they can get access to the console page. This access does not return data nor allow modification operations.
Read the publisher's advisoryAffected versions, risk and source history
Related advisories and sources
Publishers link these advisories through the identifiers shown below. A shared identifier or date alone does not tell you whether your software is affected or whether the advisories describe the same cause.
CVE-2024-27288 · CVE overview and exploitation status
cve-program · CVE-2024-27288
- https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp
- https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts
euvd · EUVD-2024-0784
- https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp
- https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts
nvd · CVE-2024-27288
- https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts
- https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp
osv · GHSA-26w3-q4j8-4xjp
- https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp
- https://nvd.nist.gov/vuln/detail/CVE-2024-27288
- https://github.com/1Panel-dev/1Panel/pull/4014
- https://github.com/1Panel-dev/1Panel
- https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts
osv · GO-2024-2613
Related changes
Linked by CVE identifierNo related changes are available here.